Your Firewall is Installed. Your SIEM is Running. Your EDR is Deployed. So Why isn't That the Question That Matters?
Most cybersecurity conversations stop at coverage: Do we have a firewall? Yes. Endpoint protection? Yes. Monitoring? Yes. Checklist complete.
But a checklist only tells you a tool exists — not whether it performs when a real adversary is actively trying to defeat it. Those are two very different claims, and the gap between them is where breaches happen.
This is the problem a cyber range is built to solve.
What A Cyber Range Actually Does
A cyber range is a controlled, isolated environment where organisations simulate realistic attack scenarios — DDoS, ransomware, malware deployment, botnet activity, data exfiltration, coordinated multi-vector attacks — without putting a single production system at risk.
Instead of confirming a tool is switched on, you observe how your networks, your technology stack, your processes, and your people actually behave when they're under hostile pressure. Because a network that looks fully hardened during normal operations can behave completely unpredictably once you introduce abnormal traffic volumes or simulate lateral movement across the environment. An incident response playbook that reads perfectly on paper can fall apart the moment a live exercise exposes real gaps in escalation and containment.
You don't find that out by auditing a checklist. You find it out by testing it.
Why This Matters Even More for OT and ICS Environments
This gets sharper still in environments where IT and OT intersect — industrial control systems, SCADA networks, power grid infrastructure — where traditional IT security assumptions frequently don't transfer cleanly, and where a failure isn't just a data breach, it's an operational one.
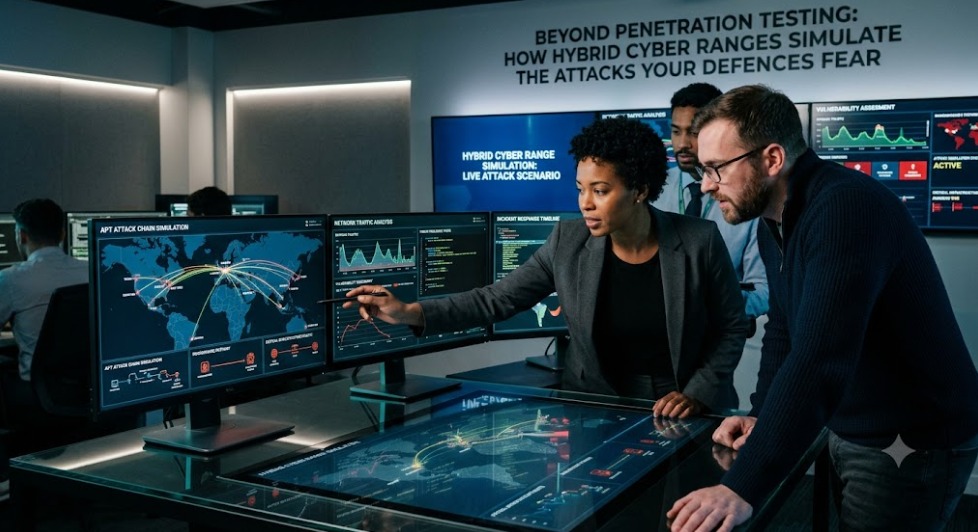
That's exactly the kind of exercise in the photo above: a live ICS Security Assessment session we ran for ERLDC, inside our own Cyber Range facility, under our NCIIPC-QCI accredited training framework. This isn't a theoretical capability. It's a room full of engineers and stakeholders working through a real simulated scenario together.
From Vulnerability Discovery to Measurable Resilience
The real value of a cyber range isn't just finding weaknesses once. It's building a repeatable discipline: rehearsing incident response, validating security architecture, running Red Team–Blue Team exercises, and tracking how your mean time to detect and mean time to respond actually improve over successive tests.
That's the shift from reactive cybersecurity to measurable resilience — and it's only possible in an environment where failure carries no real-world cost, so you can afford to find every weakness before an adversary does.
Because the question was never "do we have security tools." It's always been: when a real attack happens, will your defences perform as expected — or only as documented?